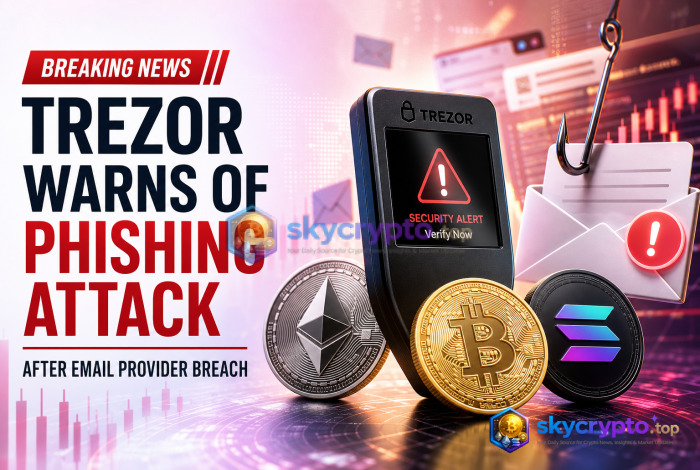
Hardware wallet manufacturer Trezor issued an urgent warning Wednesday after attackers compromised a third-party email provider to send phishing messages disguised as critical security alerts. The fraudulent emails, sent hours before Trezor's public disclosure, falsely claimed a vulnerability in STM32 microcontrollers affected one in four devices. Users were tricked into clicking links that could compromise their recovery phrases. The attack underscores growing threats targeting crypto custody infrastructure.
- Trezor confirmed hackers breached its third-party email provider to send phishing emails.
- Fake emails falsely warned of an STM32 entropy vulnerability affecting recovery phrases.
- Casa and Bitbox users may also be targeted, indicating a broader campaign.
- Trezor took down the malicious domain and urged users not to click links.
Market Reaction
Bitcoin traded at $60,250 as of 5:00 p.m. ET, down 1.2% on the day following the Trezor phishing disclosure. Traders expressed concern over the sophistication of the attack, which used valid DKIM, SPF, and DMARC signatures to appear authentic. Social media buzz intensified, with security researchers highlighting the potential impact on hardware wallet users. The incident reinforced caution among holders storing assets offline.
Altcoins tied to security and privacy tokens saw minor gains, reflecting investor focus on protective technologies. Trading volumes remained steady, suggesting limited panic selling. However, derivative markets showed increased hedging activity, with traders boosting short positions on platforms vulnerable to similar exploits. Sentiment indicators pointed to elevated fear levels, though not extreme.
Analysts noted that while the immediate market impact was muted, repeated attacks on custody providers could erode trust in self-custody solutions. Trading desks reported a uptick in inquiries about multi-signature wallets and air-gapped signing devices. Meanwhile, Bitcoin's implied volatility index rose slightly, signaling traders bracing for further developments.
Why This Happened
The phishing campaign exploited a compromise of Trezor's email service provider, allowing attackers to send messages that passed standard email authentication protocols. By impersonating a legitimate security advisory, the hackers capitalized on recent fears surrounding the Coldcard exploit, which drained over $130 million in Bitcoin earlier this year. The timing of the emails, sent just before Trezor's official warning, amplified the sense of urgency among recipients.
Security experts believe the attackers conducted reconnaissance to identify high-value targets within the crypto community. The use of authentic-looking domains and valid cryptographic signatures indicates a well-resourced operation. Furthermore, the inclusion of technical details about STM32 microcontrollers lent credibility to the deception, making it harder for users to distinguish real alerts from fake ones.
The broader macro environment has seen a surge in attacks targeting digital asset infrastructure. Regulatory uncertainty and increased institutional adoption have made crypto platforms attractive targets for cybercriminals. In this context, breaches involving third-party vendors pose systemic risks, as they provide indirect access to sensitive user data and communication channels.
Institutional and Whale Activity
On-chain data revealed no major movements from large Bitcoin holders following the Trezor disclosure. However, blockchain analytics firms detected a spike in transactions involving multi-signature wallets, suggesting whales were consolidating positions or transferring funds to more secure storage methods. Exchanges reported higher withdrawal rates for altcoins, particularly those associated with privacy features.
Futures markets reflected cautious positioning among institutional players. Open interest in Bitcoin perpetual contracts declined slightly, while funding rates turned negative for the first time in two weeks. Proprietary trading firms increased allocations to cybersecurity stocks, viewing them as defensive plays amid rising digital threats.
Corporate treasuries maintained their Bitcoin holdings unchanged, according to public filings. Nevertheless, some companies reportedly paused new crypto purchases pending enhanced due diligence on custody providers. Investment managers also adjusted portfolios to reduce exposure to firms with weak vendor security practices.
Historical Context
This incident echoes previous supply chain attacks targeting crypto infrastructure. In 2022, a similar breach of a wallet provider's update server led to the theft of approximately $500,000 worth of tokens. More recently, the Coldcard exploit highlighted vulnerabilities in hardware-based randomness generation, resulting in losses exceeding $130 million.
Past cycles have shown how security incidents can trigger sharp corrections in asset prices. During the 2018 bear market, multiple exchange hacks contributed to a prolonged downturn in Bitcoin valuation. While today's market structure is more resilient, persistent threats continue to weigh on long-term confidence in decentralized finance.
Comparing current events to historical precedents reveals evolving attack vectors. Earlier incidents primarily involved direct theft from exchanges or wallets. Modern campaigns increasingly exploit trust relationships and technical legitimacy, making prevention more challenging without comprehensive oversight of all service providers.
What Traders Are Watching
- Bitcoin price support at $59,800 and resistance at $61,200.
- Trezor stock reaction if listed; otherwise monitor cybersecurity ETFs.
- Upcoming Fed meeting minutes for signals on rate path and risk appetite.
- On-chain metrics tracking multi-sig wallet usage and exchange flows.
- New phishing domain registrations linked to crypto projects or vendors.
Disclaimer: This article is provided for informational and educational purposes only and does not constitute financial, investment, or trading advice. Digital assets carry significant market risk.

Comments
You must be logged in to post a comment.
Login or Register